When CMMC Compliance Costs More Than the Contract: The Case for Reform
The Department of Defense’s July 2026 suspension of Phase II didn’t happen because of a policy disagreement. It happened...
4 min read

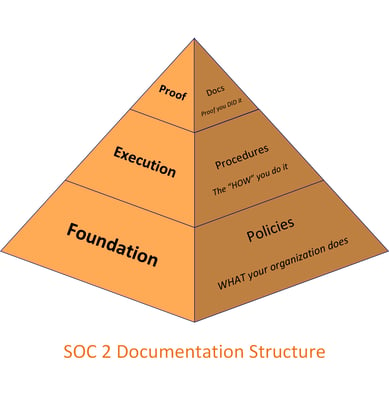
Wondering what to expect as you go through your first SOC 2 Audit? This post covers each step of the process. At every step, keep in mind that the entire goal of the SOC 2 audit is to measure how well your organization handles its business processes, users, data (proprietary, customer, etc.). A SOC 2 security audit can help your company demonstrate it has applied the best control mechanism to assure security, availability, processing integrity, confidentiality, and privacy of client data. This then generates trust and confidence from inquiring vendors and prospective customers.
Contents:
|
Traditional Approach |
Silent Sector’s Approach |
|
“SOC 2 is just a sticker” |
Security is inserted into processes and culture thereby eliminating the false sense of security generated from automated reporting tools |
|
Ultimately not really that secure |
Evidence of improved security generated from ongoing processes and annual refreshes |
|
Audit hectic and disruptive |
Audit is smooth and flows conservatively |
Contact Silent Sector for an initial consultation to prepare for your SOC 2 audit.
The Department of Defense’s July 2026 suspension of Phase II didn’t happen because of a policy disagreement. It happened...
On July 13, 2026, the Department of Defense (DoD) announced the immediate suspension of CMMC Phase II requirements,...
If you’re an IT leader who just received a risk assessment report that’s 40 pages long with a list of findings you’re not...
If your organization is using—or planning to use—generative AI tools, you’re already carrying new risk. The major risks...